Solana-based cryptocurrency wallet Solflare has tightened its internal security controls, restricting infrastructure access and software changes following a series of major attacks across the crypto industry.
Summary
- Solflare has restricted access to its infrastructure and code following recent cryptocurrency security incidents.
- Co-founder Vidor said all changes now require multiple approvals, while the team has paused new additions.
- An October security incident involving a third-party staking provider affected keys used by Solflare’s validator.
- Solflare said no customer funds were stolen, although affected users temporarily stopped earning staking rewards.
- The wallet has extended its validator migration deadline to November 30 and promised to cover missed rewards from October 26 to November 1.
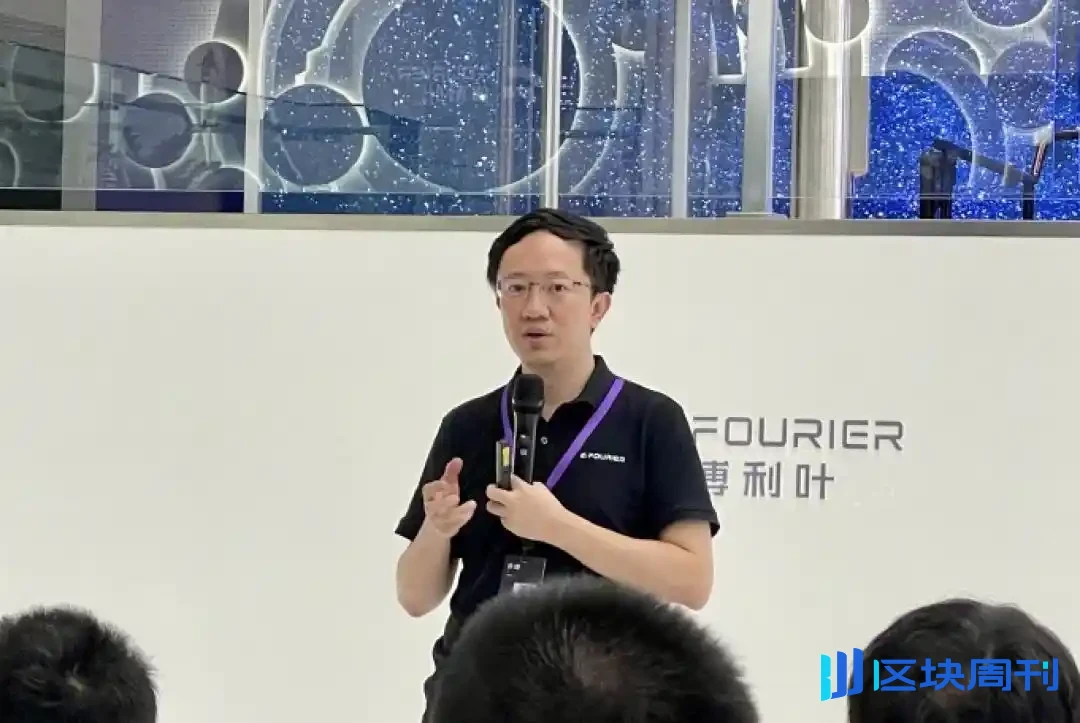
In a November 2 statement, Solflare co-founder Vidor said the development team had entered “bunker mode,” introducing multiple approval requirements and stopping new additions to its systems.
“After the month this industry just had, access to our infra and code is shut down, every change needs multiple approvals, and nothing new gets in,” Vidor wrote.
He acknowledged that the restrictions would affect the company’s development schedule, adding, “It slows us down and I’m fine with that.”
Solflare tightens access to infrastructure and code
Solflare’s latest security measures focus on controlling who can access its systems and authorize changes to its software.
Under the new arrangements, developers must secure multiple approvals before making changes to infrastructure or code. The team has suspended new additions while the restrictions remain in place.
The announcement followed an October 29 Binance security breach involving approximately $6.3 billion in affected cryptocurrency assets.
As crypto.news previously reported, Binance’s preliminary investigation identified a potentially compromised engineer’s laptop as one possible entry point.
The exchange said attackers may have gained access to internal infrastructure used to authorize cryptocurrency withdrawals.
Another recent incident involved Keystone wallet customer records, which exposed buyers’ personal information after unauthorized access to the hardware wallet manufacturer’s website.
Keystone said private keys and recovery phrases remained unaffected, although the exposed customer information created additional phishing concerns.
Solflare’s restrictions concern its own operational systems, while its recent staking disruption originated with an outside service provider.
Solflare validator incident interrupts staking rewards
On October 27, Solflare disclosed that its third-party staking provider had reported a security incident involving keys associated with the wallet’s Solana validator.
“Our staking provider has notified us of a security incident on their side,” the company said in its initial notice.
The affected validator stopped producing staking rewards while the provider investigated the incident.
Solflare explained that users’ delegated SOL remained in their individual stake accounts, which are controlled by their private keys.
“Your SOL is safe,” the wallet said, adding that “No user funds were touched.”
The company emphasized that holding validator keys does not give an operator authority to transfer SOL from customers’ delegated staking accounts.
Blockchain monitoring data cited by Unchained showed approximately 1.56 million SOL delegated to the affected validator on October 28.
The validator had stopped voting and was no longer generating rewards for those delegators.
A separate October 29 investigation by Bitquery traced unauthorized transfers from keys associated with several Solana validators, including Solflare’s.
The blockchain analytics firm estimated that the attacker transferred assets worth approximately $135,000 from five validators.
Its findings distinguished assets held by validator operators from customer funds held in delegated staking accounts.
Solflare extends staking migration deadline to November 30
Following the incident, Solflare established a replacement validator and began directing affected users to transfer their delegated SOL.
The company initially set November 1 as the deadline for users seeking compensation for missed staking rewards.
However, its latest announcement extended the migration deadline to November 30.
“You now have until November 30 to move your stake to the new Solflare validator,” the wallet told users.
Solflare confirmed that it would cover staking rewards missed between October 26 and November 1 for users completing the migration.
The company has introduced an in-app process intended to help customers move their stake to the replacement validator.
Users can update their Solflare application and follow the migration instructions to complete the process.
Staking rewards resume once the transferred SOL becomes active on the new validator.
Solana’s staking system processes activation and deactivation through network epochs, meaning some transfers may require additional time before generating rewards.
Solflare warns users against fake migration links
During its initial security announcement, Solflare warned customers that scammers could exploit the validator migration to distribute fraudulent instructions.
The wallet said the process would take place exclusively through its official application.
“Migration will only happen through the Solflare app. We will never DM you or send you a link,” the company stated.
The warning followed the provider incident, which required users to change validators to restore staking rewards.
Solflare’s response comes during a period when other cryptocurrency businesses have introduced emergency restrictions following security breaches.
Brazilian exchange Mercado Bitcoin recently suspended customer withdrawals after identifying unauthorized activity involving its systems.
For Solflare users, the latest instructions remain focused on completing the validator migration through the wallet application before November 30.
The company has committed to covering the specified six-day period of missed staking rewards for customers who complete that process.